Description
Build confidence reading network captures by working through packet-analysis exercises in Wireshark. The course uses trace files and questions to connect protocol details with troubleshooting, showing how captured traffic can help explain a network problem or investigate a security incident.
Alongside the analysis tasks, the lessons cover the interface itself: custom columns, display filters, colouring rules and layout adjustments. DHCP, DNS and TCP/IP provide the protocol context, while the assignments encourage learners to inspect the evidence in a capture before comparing their conclusions with the explanation.
What you will learn
- Capture and interpret traffic in Wireshark.
- Inspect DHCP, DNS and TCP/IP exchanges.
- Customise columns, filters and colouring rules for analysis.
Course specifications
- Publisher
- Udemy
- Instructors
- Experts with David Bombal, Chris Greer, David Bombal
- Language
- English
- Level
- Beginner
- Duration
- 4 hours and 25 minutes
- Subtitle
- English
- Quality
- 1080p
- Edition
- 2025-8
Course topics
View course topics
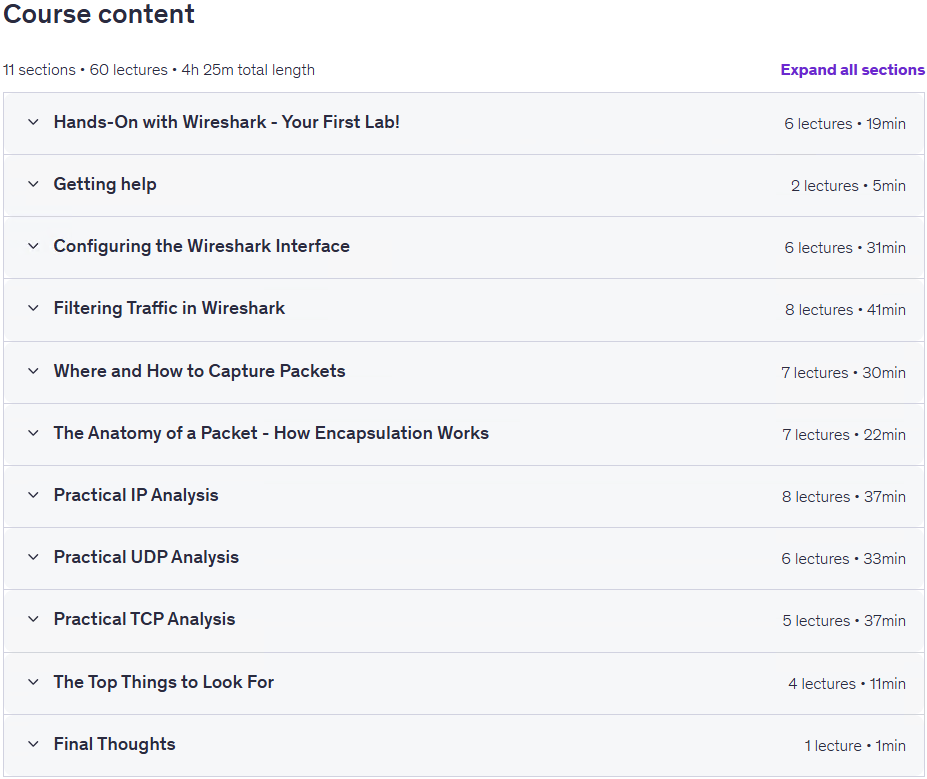
The course topics image is temporarily unavailable.
Prerequisites
- Basic networking knowledge, including switching and routing.
Pictures
This picture is temporarily unavailable.
Introduction video
How to open the files
Keep all parts of the same edition together before extracting the first archive. Open the included course media with a compatible player.
Download resources
Choose one edition and keep its parts together. Alternate providers are available when listed.
2025-8 · 1080p
Direct downloads
2025-8 · 1080p
Size
4.88 GB
Leave a Reply
Signed-in member comments appear immediately.