Description
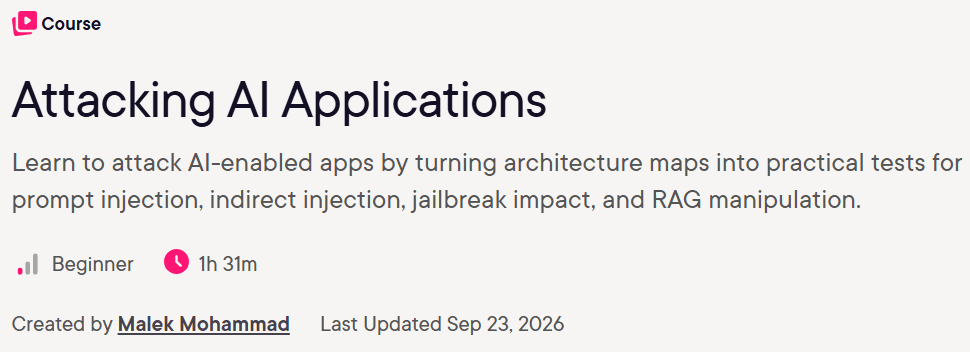
Malek Mohammad examines security testing for applications that connect language models with documents, APIs, user information and business workflows. The course starts by mapping those connections into an attack surface and uses that map to plan assessments of direct and indirect prompt injection.
The later material explores the security impact of jailbreaks and manipulated retrieval inputs, including controlled tests with poisoned source documents. It distinguishes a model responding unexpectedly from an application weakness with a demonstrable consequence. Documenting the test and explaining its impact are treated as essential parts of an AI-application assessment.
Intended audience: Application-security assessors, penetration testers, security researchers and AI-system engineers.
What you will learn
- Map an AI application's architecture into assessment targets.
- Evaluate direct and indirect prompt-injection behavior.
- Examine retrieval manipulation in controlled security tests.
- Document findings and distinguish behavioral bypasses from security impact.
Course specifications
- Publisher
- Pluralsight
- Instructors
- Malek Mohammad
- Quality
- 1080p
- Level
- Beginner
- Duration
- 1 hour and 31 minutes
- Subtitle
- English
- Edition
- 2026-9
Course topics
View course topics
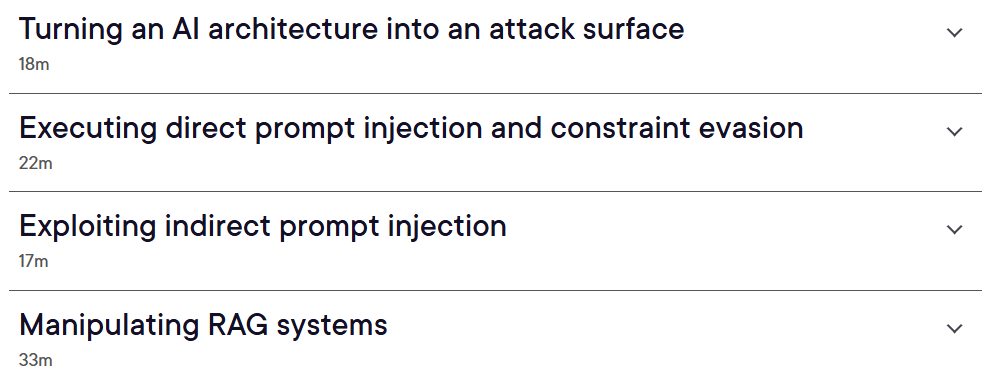
The course topics image is temporarily unavailable.
Pictures
This picture is temporarily unavailable.
Introduction video
How to open the files
Keep all parts of the same edition together before extracting the first archive. Open the included course media with a compatible player.
Download resources
Choose one edition and keep its parts together. Alternate providers are available when listed.
Size
238 MB
Leave a Reply
Signed-in member comments appear immediately.